[email protected]
Back to All Articles
Environmental, Health & Safety, Supply Chain & Regulatory

Compliance & EHS Insights

Comprehensive guides on EHS compliance, OSHA regulations, EPA requirements, supply chain quality, supplier auditing, and regulatory frameworks for manufacturers. From CFATS to ISO 14001 and ISO 45001 integration.

15 articlesPowered by ComplianceFortress
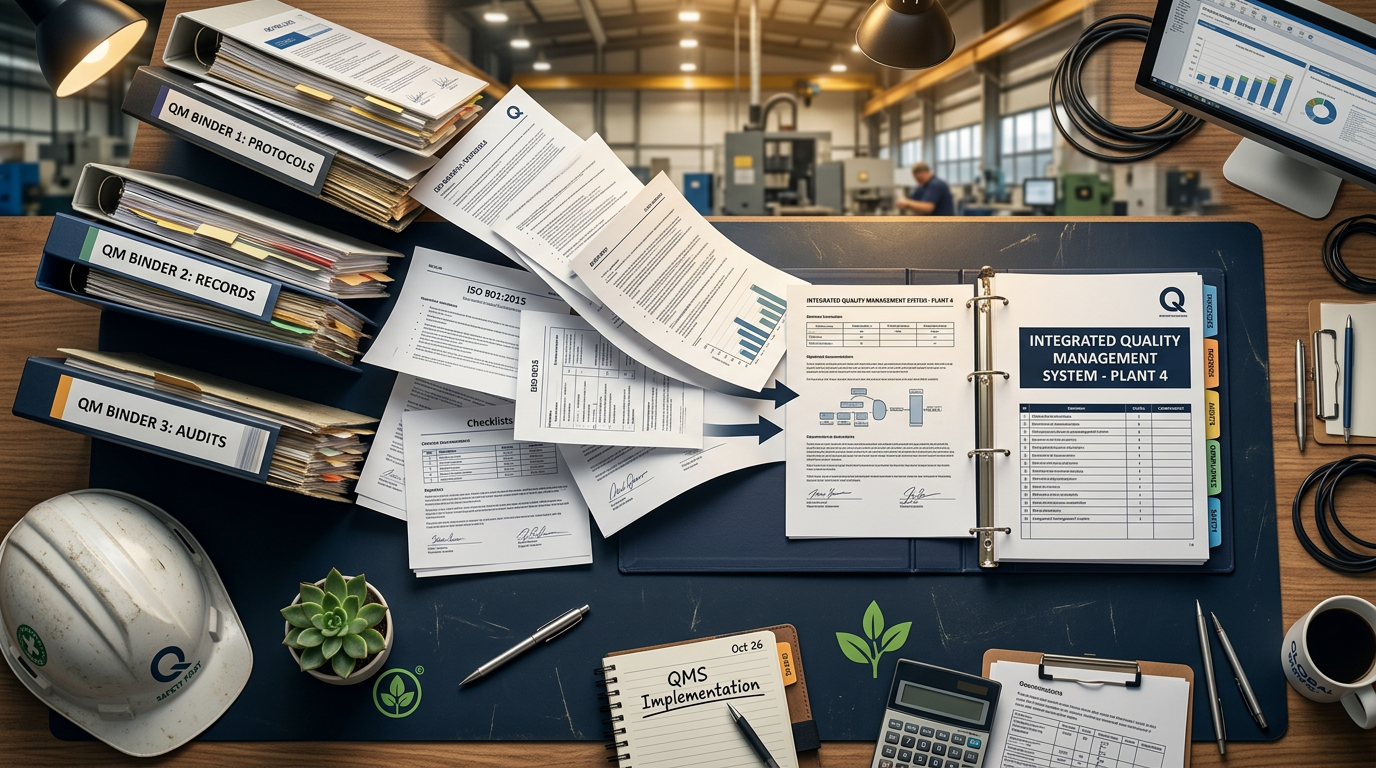
Integrated Management System for ISO 9001, 14001 and 45001: Stop Running Three Systems
Compliance & EHS•13 min read•Exceleor Team

Integrated Management System for ISO 9001, 14001 and 45001: Stop Running Three Systems

Three standards, three manuals, three audit schedules, three management reviews — and one small team trying to keep all of it alive. ISO 9001, ISO 14001 and ISO 45001 share the same high-level structure, which means most of that duplication is optional. This guide shows what an integrated management system looks like, what to combine first, what must stay separate, and how to integrate without disrupting your certifications.

Integrated Management SystemISO 9001ISO 14001
September 26, 2026
Supplier Nonconformance: What to Do When a Key Supplier Fails (Containment to Corrective Action)
Compliance & EHS•13 min read•Exceleor Team

Supplier Nonconformance: What to Do When a Key Supplier Fails (Containment to Corrective Action)

A key supplier just shipped nonconforming parts, failed an audit, or went quiet on a critical order. Your customer is waiting and your line may stop. This guide covers the first 24 hours, containment that actually protects your customer, how to issue a supplier corrective action request that gets a real answer, when to consider a second source, and how to build the supplier controls ISO 9001 Clause 8.4 expects so it doesn't happen again.

Supplier NonconformanceSupplier Corrective ActionSCAR
September 26, 2026
We Got an OSHA Recordable: What to Do in the First 48 Hours
Compliance & EHS•13 min read•Exceleor Team

We Got an OSHA Recordable: What to Do in the First 48 Hours

Someone got hurt at your plant. The adrenaline is high, the facts are incomplete, and the clock is running. This guide walks through the first 48 hours: caring for the employee and securing the scene, deciding whether the case is OSHA recordable or reportable, the 8-hour and 24-hour reporting rules, completing the OSHA 300 log and 301 form, running an investigation that finds real causes, and connecting it all to your ISO 45001 system.

OSHA RecordableOSHA 300 LogIncident Investigation
September 26, 2026
Supply Chain Resilience and the ISO Quality Connection: Why They Can't Be Separated
Compliance & EHS•9 min read•Exceleor Team

Supply Chain Resilience and the ISO Quality Connection: Why They Can't Be Separated

Your ISO management system is only as strong as your supply chain. SupplySourceSync provides end-to-end supply chain consulting while Exceleor ensures your quality management system addresses supplier controls.

Supply ChainISO 9001SupplySourceSync
March 8, 2026
EHS Compliance for Manufacturers: The Complete Guide to Environmental, Health & Safety
Compliance & EHS•13 min read•Exceleor Team

EHS Compliance for Manufacturers: The Complete Guide to Environmental, Health & Safety

EHS compliance is not optional—it's the cost of doing business in manufacturing. ComplianceFortress provides independent third-party auditing across OSHA, EPA, CFATS, and state regulations.

EHS ComplianceComplianceFortressOSHA
March 6, 2026
5 Things Your Supplier Quality Auditor Wishes You Knew Before the Audit
Compliance & EHS•7 min read•Exceleor Team

5 Things Your Supplier Quality Auditor Wishes You Knew Before the Audit

As former OEM supplier quality auditors, we've seen the same mistakes hundreds of times.

Supplier QualityAuditsCorrective Action
February 5, 2026
ISO 14001 + ISO 45001 Integration: Building a Unified EHS Management System
Compliance & EHS•10 min read•Exceleor Team

ISO 14001 + ISO 45001 Integration: Building a Unified EHS Management System

Environmental (ISO 14001) and occupational health & safety (ISO 45001) management systems share the same Annex SL structure — making integration not just possible, but highly efficient. An integrated EHS management system reduces documentation duplication by up to 40%, streamlines internal audits, and provides a single framework for managing environmental and safety risks. We combine these with ComplianceFortress EHS auditing to deliver complete regulatory compliance.

ISO 14001ISO 45001EHS
March 13, 2026
OSHA Compliance for Manufacturers: The Complete Guide to Avoiding Citations and Building Safety Culture
Compliance & EHS•11 min read•Exceleor Team

OSHA Compliance for Manufacturers: The Complete Guide to Avoiding Citations and Building Safety Culture

OSHA citations in manufacturing averaged $15,625 per serious violation in 2025, with willful violations reaching $156,259. But the real cost is in lost productivity, workers comp premiums, and employee turnover. We cover the OSHA standards most commonly cited in manufacturing (lockout/tagout, machine guarding, hazard communication, respiratory protection), how to build a proactive safety program that satisfies ISO 45001 and OSHA simultaneously, and how ComplianceFortress helps manufacturers create safety cultures that go beyond compliance.

OSHAManufacturing SafetyISO 45001
March 24, 2026
Environmental Permits for Manufacturers: Air, Water, Waste & What Inspectors Look For
Compliance & EHS•12 min read•Exceleor Team

Environmental Permits for Manufacturers: Air, Water, Waste & What Inspectors Look For

Environmental compliance for manufacturers goes far beyond ISO 14001 certification. Air permits (Title V, minor source), NPDES water discharge permits, RCRA hazardous waste generator status, SPCC plans, and Tier II reporting all require ongoing management. We break down the permitting landscape for manufacturers, explain what EPA and state inspectors actually look for during inspections, and how an integrated ISO 14001 + permit compliance program reduces both risk and administrative burden.

Environmental PermitsEPAISO 14001
March 24, 2026
What Happens During an ISO Audit? A Step-by-Step Guide From an Active 3rd Party Auditor
Compliance & EHS•15 min read•Exceleor Team

What Happens During an ISO Audit? A Step-by-Step Guide From an Active 3rd Party Auditor

Most manufacturers dread ISO audits because they do not know what to expect. As an active 3rd party auditor who conducts certification, surveillance, and recertification audits across 9+ standards, we pull back the curtain on exactly what happens from the moment the auditor walks in the door. We cover the complete audit lifecycle: Stage 1 documentation review (what auditors look for in your quality manual, procedures, and records), Stage 2 on-site assessment (how auditors select processes to audit, what questions they ask operators, how they evaluate competence), the closing meeting (how findings are categorized as major nonconformities, minor nonconformities, or opportunities for improvement), and the post-audit corrective action process. We share the 10 most common audit findings we write across all standards, the 5 things that impress auditors most, and a practical pre-audit checklist your team can use to prepare. This is the insider perspective you cannot get from someone who has never held a clipboard on the other side of the audit table.

ISO AuditAudit ProcessISO 9001 Audit
June 5, 2026
EU AI Act Compliance for US Manufacturers: What You Must Know Before 2027
Compliance & EHS•16 min read•Exceleor Team

EU AI Act Compliance for US Manufacturers: What You Must Know Before 2027

If you sell products into Europe that contain AI — machine vision systems, smart sensors, autonomous robots, AI-powered quality inspection — the EU AI Act applies to you regardless of where you are headquartered. With enforcement beginning in phases through 2027, US manufacturers face a compliance cliff. We explain the 4 risk tiers, which manufacturing AI applications fall into "high risk" (hint: most of them), the documentation requirements that mirror ISO 42001, and the practical steps to achieve compliance without disrupting your operations. The penalties for non-compliance start at €35 million or 7% of global revenue.

EU AI ActAI ComplianceISO 42001
July 15, 2026
How to Build an Internal Audit Program That Actually Finds Problems
Compliance & EHS•13 min read•Exceleor Team

How to Build an Internal Audit Program That Actually Finds Problems

Most internal audit programs are theater — a checklist exercise that confirms everything is fine right up until the registrar finds three major nonconformities. As active third-party auditors, we build internal audit programs that surface real issues before they reach a certification body or a customer. This guide covers how to build a risk-based audit schedule that focuses effort where failure hurts most, how to train auditors to ask open-ended questions instead of yes/no checklist items, how to write findings that drive corrective action rather than defensiveness, and how to use audit results as management-review input. We share the difference between a compliance audit and a value-adding audit, the seven habits of auditors who consistently find the issues that matter, and a practical maturity model to move your program from box-checking to genuine risk reduction.

Internal AuditsAudit ProgramISO 9001
April 14, 2026
Building a Supplier Audit Program: How to Control Quality You Do Not Own
Compliance & EHS•13 min read•Exceleor Team

Building a Supplier Audit Program: How to Control Quality You Do Not Own

Your quality is only as strong as your weakest supplier — yet most manufacturers audit suppliers reactively, only after a bad lot has already reached the floor. A proactive supplier audit program turns your supply base from a liability into a competitive advantage. We cover how to segment suppliers by risk and criticality so audit effort goes where it matters, how to build supplier audit checklists that go beyond confirming ISO certificates to actually verifying process capability, how to run effective on-site and remote supplier audits, and how to use scorecards and corrective-action tracking to drive supplier improvement over time. This is the program SupplySourceSync builds for manufacturers who need to satisfy ISO 9001 Clause 8.4 requirements while genuinely reducing incoming defects and supply risk.

Supplier AuditsSupplier QualitySupplySourceSync
June 18, 2026
Root Cause Analysis for CAPA: Why Your Corrective Actions Keep Failing
Compliance & EHS•13 min read•Exceleor Team

Root Cause Analysis for CAPA: Why Your Corrective Actions Keep Failing

If the same nonconformities keep reappearing in your audits, your corrective action process is treating symptoms, not causes. Weak root cause analysis is the number-one reason CAPA systems generate paperwork without preventing recurrence. As auditors, we see it constantly — a containment action dressed up as a corrective action, a "retrained the operator" close-out that fixes nothing. We break down how to run root cause analysis that actually works: when to use 5-Why versus fishbone versus fault-tree analysis, how to distinguish occurrence causes from escape causes from systemic causes, how to verify effectiveness before closing a CAPA, and how to build a CAPA process that satisfies ISO 9001, IATF 16949, and ISO 13485 requirements while genuinely driving continual improvement. Includes the questions we ask to test whether a root cause is real.

Root Cause AnalysisCAPACorrective Action
July 8, 2026
A Supply Chain Risk Assessment Framework for Manufacturers
Compliance & EHS•13 min read•Exceleor Team

A Supply Chain Risk Assessment Framework for Manufacturers

Recent years taught every manufacturer that supply chain risk is business risk — a single-source component or a struggling supplier can shut down your production overnight. Yet most manufacturers still manage supply risk by intuition rather than a structured framework. We lay out a practical supply chain risk assessment process: how to map your supply base and identify single points of failure, how to score suppliers across financial, operational, geographic, and quality dimensions, how to build early-warning indicators that flag trouble before it becomes a disruption, and how to develop mitigation strategies from dual-sourcing to strategic inventory. Grounded in ISO 9001 Clause 8.4 requirements and built for the real world, this is the framework SupplySourceSync uses to turn fragile supply chains into resilient ones.

Supply Chain RiskRisk AssessmentSupplySourceSync
September 23, 2026

Ready to Explore the Ecosystem?

Our family of 8 specialized brands is ready to help your manufacturing operation achieve excellence across quality, compliance, operations, and beyond.