[email protected]
Back to All Articles
ISO 27001, CMMC, SOC 2 & Data Protection

Cybersecurity & Information Security Insights

Deep-dive articles on ISO 27001 implementation, CMMC readiness, SOC 2 alternatives, and information security for manufacturers. Our team holds ISO 27001 certification — we don't just consult, we live it. From ISMS building to ransomware defense.

10 articlesPowered by ComplianceFortress
Data Center Security Audits: Why the Real Value Is in Your Processes, Not Your Locks
Cybersecurity & Information Security•10 min read•Exceleor Team

Data Center Security Audits: Why the Real Value Is in Your Processes, Not Your Locks

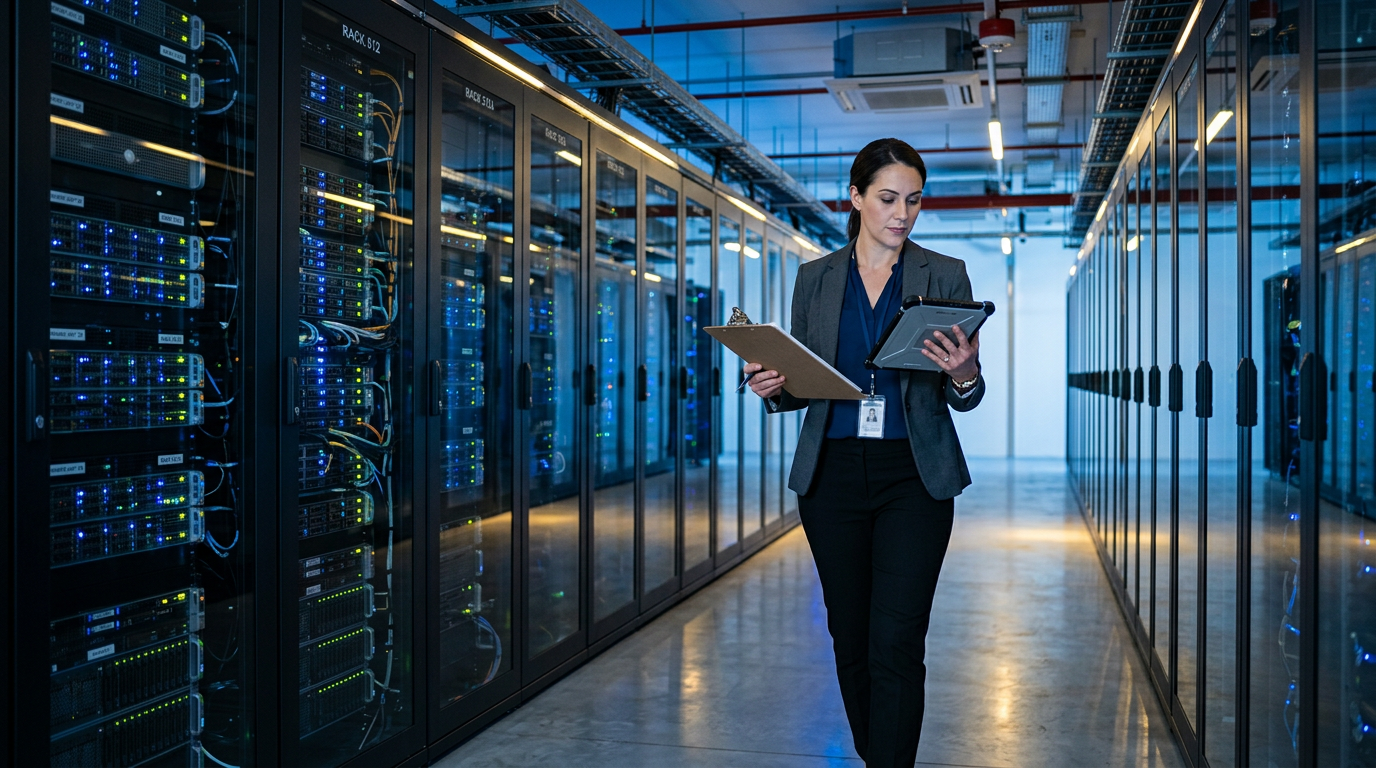
Most people picture a data center security audit as a walk past badge readers, cameras, and locked cages. Those controls matter, but they are the visible end of a chain of processes: who approves access, how changes are made, how maintenance is scheduled, how incidents are handled, and how vendors are supervised. When one of those processes breaks, the lock on the door doesn't help. This article explains what a security audit really tests in a data center, and why the lasting benefit is a set of processes that work the same way every time.

Data Center AuditData Center SecuritySecurity Audit
September 26, 2026
What a Data Center Security Audit Actually Examines: A Process-by-Process Guide
Cybersecurity & Information Security•12 min read•Exceleor Team

What a Data Center Security Audit Actually Examines: A Process-by-Process Guide

If a data center security audit is coming, it helps to know what the auditor will actually do. This guide walks through the eight processes an auditor typically follows from start to finish: the access lifecycle, visitor and contractor control, change management, maintenance, environmental monitoring, backup and recovery, incident response, and supplier oversight. For each one, you'll see what the auditor asks, what evidence they sample, and the weak points we find most often. Use it as a self-check before the auditor arrives.

Data Center Audit ChecklistData Center SecurityAccess Control
September 26, 2026
ISO 27001 for Manufacturers: Protecting Your Intellectual Property & Customer Data
Cybersecurity & Information Security•8 min read•Exceleor Team

ISO 27001 for Manufacturers: Protecting Your Intellectual Property & Customer Data

As manufacturing becomes increasingly digital, cybersecurity is essential. ISO 27001 is the framework to protect your data.

ISO 27001CybersecurityInformation Security
January 12, 2026
ISO 27001 vs SOC 2: Which Security Framework Is Right for Your Organization?
Cybersecurity & Information Security•12 min read•Exceleor Team

ISO 27001 vs SOC 2: Which Security Framework Is Right for Your Organization?

ISO 27001 and SOC 2 are both information security frameworks — but they serve different purposes. ISO 27001 is an internationally recognized certification valid for 3 years across 160+ countries. SOC 2 is a US-specific audit report valid for 12 months. Our team holds ISO 27001 certification and can objectively evaluate both paths. Here's how to choose the right framework based on your customer base, geographic footprint, and contract requirements.

ISO 27001SOC 2Cybersecurity
March 28, 2026
CMMC and ISO 27001: The 70% Overlap That Saves Defense Contractors Time and Money
Cybersecurity & Information Security•14 min read•Exceleor Team

CMMC and ISO 27001: The 70% Overlap That Saves Defense Contractors Time and Money

CMMC Level 2 requires 110 NIST 800-171 controls. Approximately 70% of those controls map directly to ISO 27001 Annex A. That means organizations starting with ISO 27001 get a globally recognized certification NOW while building most of their CMMC foundation simultaneously. We break down the control mapping, identify the remaining 30% gap, and outline the most cost-effective path to dual compliance.

CMMCISO 27001NIST 800-171
March 27, 2026
Manufacturing Is the #1 Ransomware Target: Here's What You Need to Know
Cybersecurity & Information Security•10 min read•Exceleor Team

Manufacturing Is the #1 Ransomware Target: Here's What You Need to Know

Manufacturing has surpassed financial services as the most-attacked industry globally, with ransomware incidents increasing 300% since 2020. CNC programs, customer specifications, pricing data, and OT systems are all targets. The average manufacturing breach costs $4.73M. ISO 27001 provides the systematic, risk-based approach to information security that covers people, processes, and technology — the three pillars attackers exploit.

RansomwareManufacturing CybersecurityISO 27001
March 26, 2026
NIST SP 800-171 vs. ISO 27001: Which Framework Do Defense Contractors Actually Need?
Cybersecurity & Information Security•14 min read•Exceleor Team

NIST SP 800-171 vs. ISO 27001: Which Framework Do Defense Contractors Actually Need?

Defense contractors face a confusing compliance landscape: DFARS requires NIST SP 800-171, CMMC mandates third-party assessment, and customers increasingly demand ISO 27001 certification. Do you need both? Can you implement one and satisfy the other? We map the 110 NIST 800-171 security requirements against ISO 27001 Annex A controls, quantify the 70% overlap, identify the gaps in each direction, and provide a practical implementation roadmap for defense manufacturers who need to satisfy both frameworks efficiently.

NIST 800-171ISO 27001Defense Contractors
March 23, 2026
Zero Trust Architecture for Manufacturing: Securing OT Networks Without Stopping Production
Cybersecurity & Information Security•12 min read•Exceleor Team

Zero Trust Architecture for Manufacturing: Securing OT Networks Without Stopping Production

Operational Technology (OT) networks in manufacturing were designed for availability, not security. But with ransomware attacks on manufacturers increasing 87% year-over-year, the traditional air-gap approach no longer works. We explain how to implement Zero Trust Architecture in manufacturing environments — from network microsegmentation and identity-based access to OT/IT convergence strategies — without disrupting production uptime or breaking legacy SCADA/PLCs.

Zero TrustOT SecurityManufacturing Cybersecurity
March 23, 2026
Machine Learning Quality Inspection: Building Trust and Compliance Through ISO 42001
Cybersecurity & Information Security•15 min read•Exceleor Team

Machine Learning Quality Inspection: Building Trust and Compliance Through ISO 42001

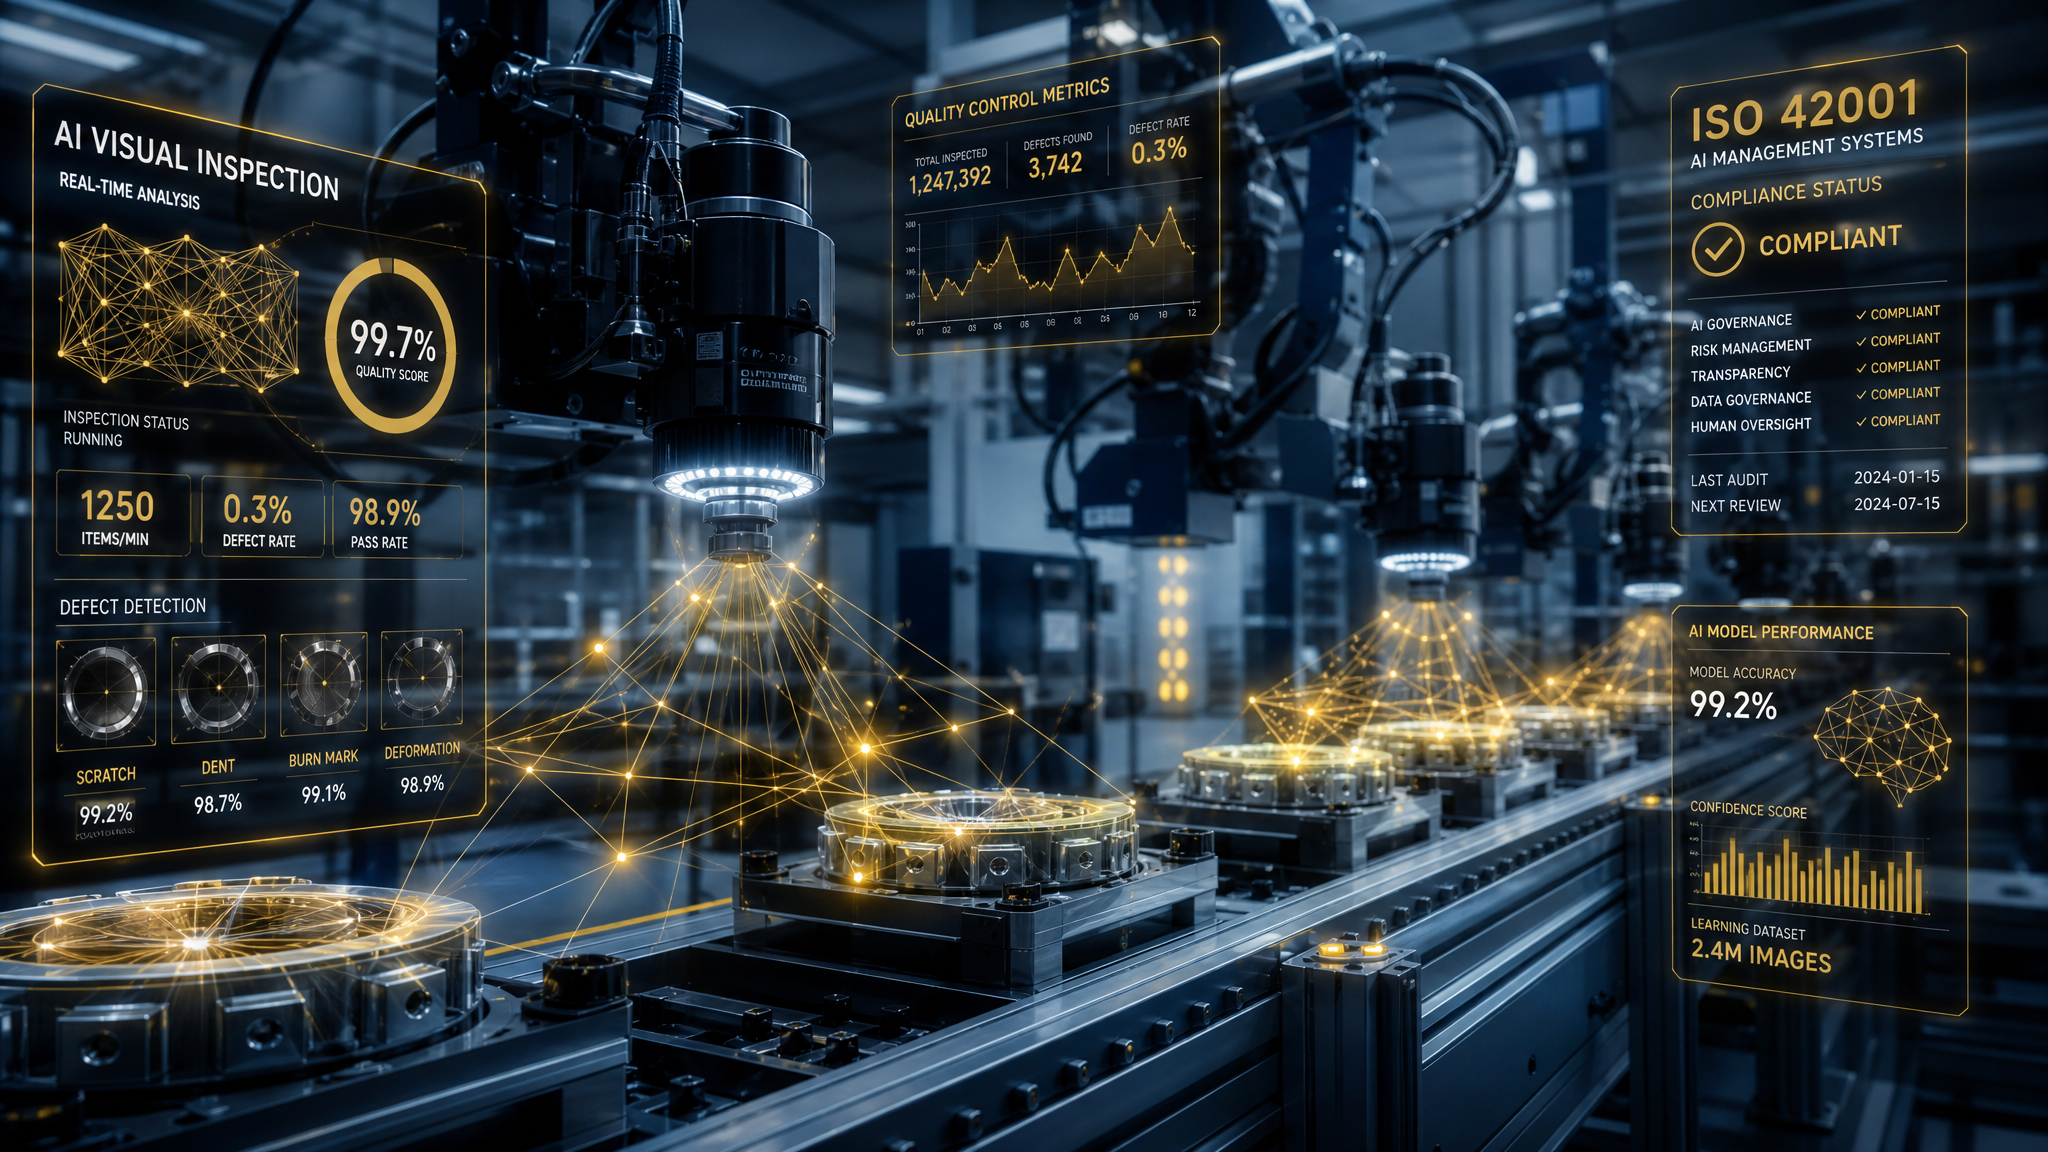
Machine learning visual inspection systems can detect defects 10x faster than human inspectors — but can you prove to your customers, auditors, and regulators that your AI makes reliable decisions? ISO 42001 provides the framework to document AI training data provenance, validate model accuracy against human baselines, establish drift detection protocols, and create the audit trail that proves your AI inspection system is trustworthy. We cover the 7 critical elements of an AI quality inspection governance program, real examples from aerospace and automotive manufacturers, and how to satisfy customer quality requirements like AS9100 and IATF 16949 when AI is part of your inspection process.

ISO 42001Machine LearningQuality Inspection
August 15, 2026
Cybersecurity Awareness Training for Manufacturing Employees: Your Weakest Link Is Human
Cybersecurity & Information Security•11 min read•Exceleor Team

Cybersecurity Awareness Training for Manufacturing Employees: Your Weakest Link Is Human

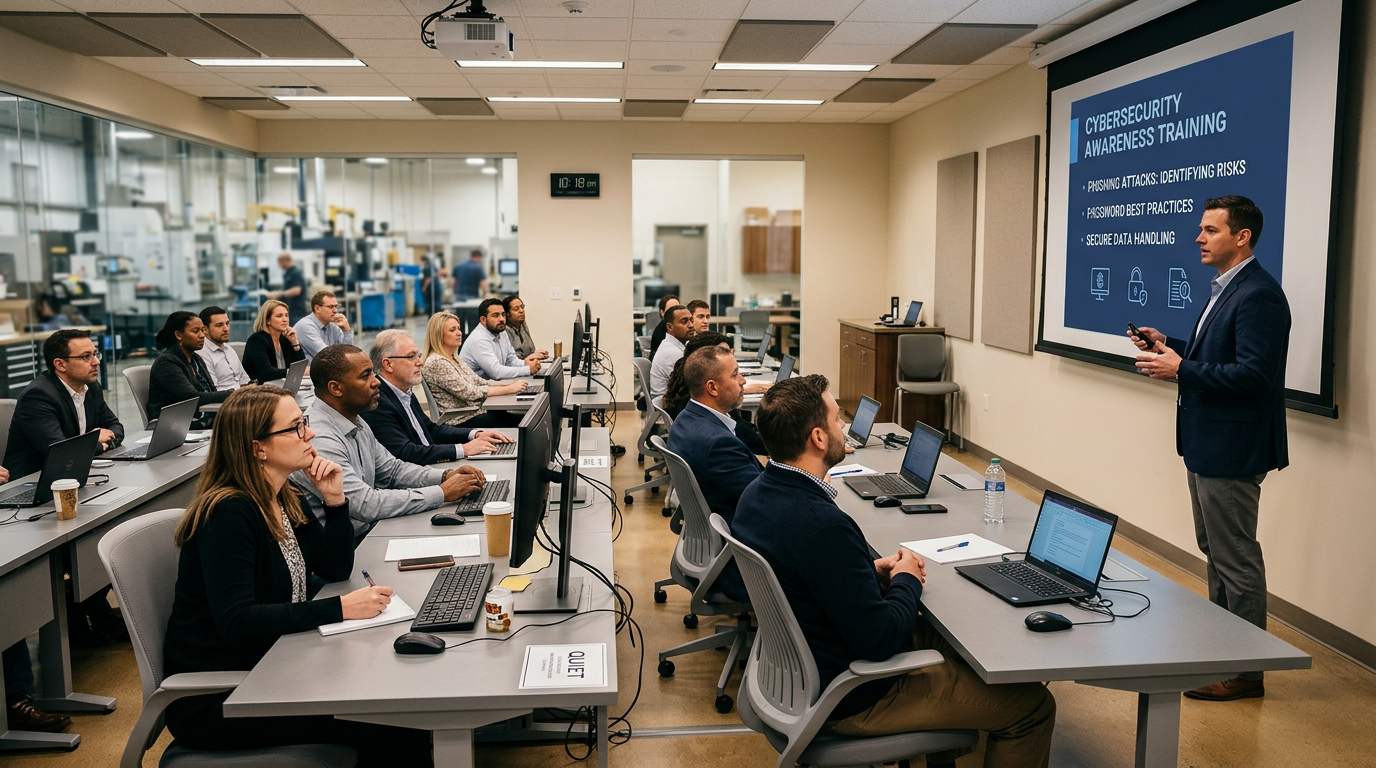
The most sophisticated firewall in the world will not stop an employee who clicks a phishing link or plugs an unknown USB drive into a controls PC. In manufacturing — where IT and OT networks increasingly connect — human error is the leading cause of security incidents. Yet most manufacturers treat security awareness as an annual video nobody watches. We explain how to build a cybersecurity training program that actually changes behavior: how to tailor training to manufacturing-specific threats like OT intrusion and supply-chain compromise, how to run phishing simulations that teach instead of shame, how to satisfy the awareness requirements in ISO 27001, CMMC, and NIST 800-171, and how to measure whether your training is working. Because in a ransomware era, an unprepared workforce is an unlocked door.

Cybersecurity TrainingSecurity AwarenessISO 27001
September 11, 2026

Ready to Explore the Ecosystem?

Our family of 8 specialized brands is ready to help your manufacturing operation achieve excellence across quality, compliance, operations, and beyond.