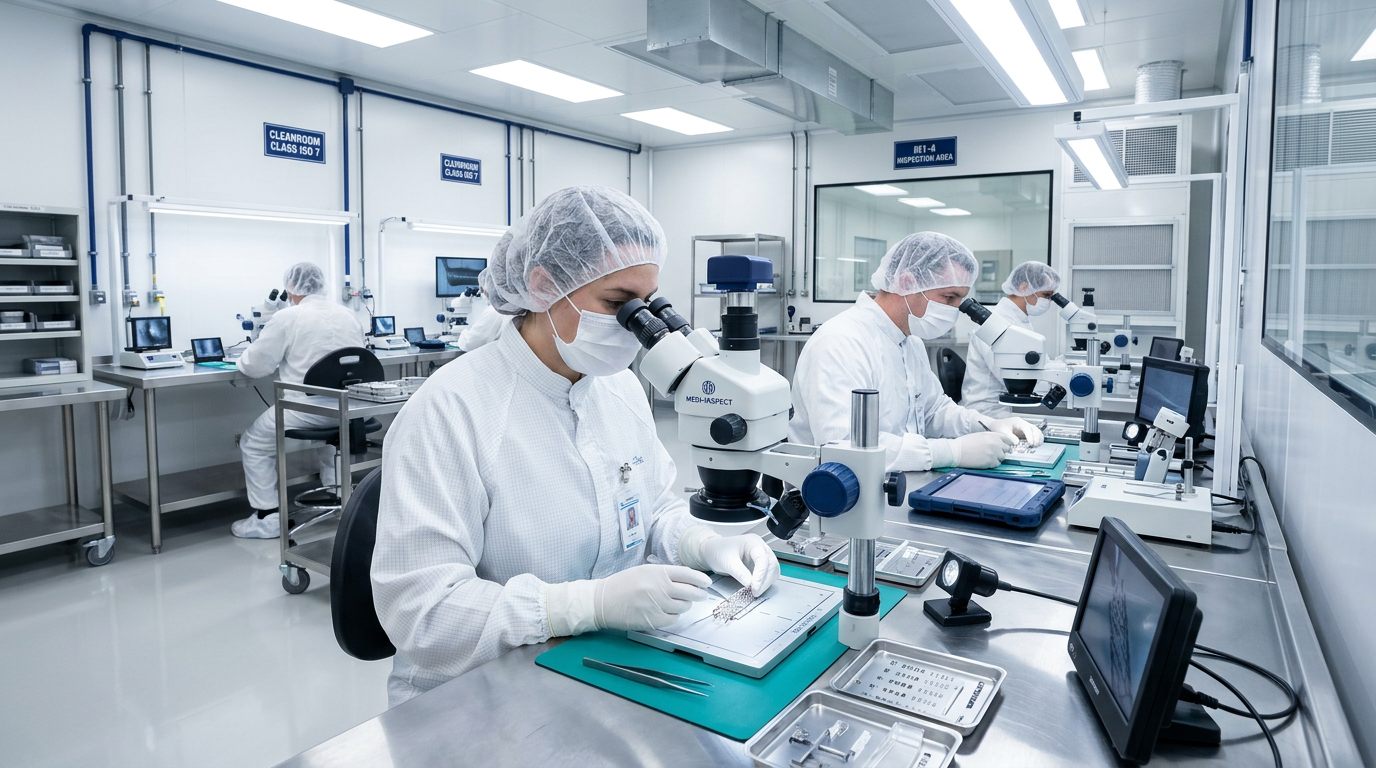
Internal audits under ISO 13485 carry higher stakes than most standards — a weak audit program does not just risk a nonconformity, it risks patient safety and FDA scrutiny. Medical device manufacturers must audit not only for conformity but for the effectiveness of risk management, design controls, and post-market surveillance. We cover how to build an ISO 13485 internal audit program that satisfies both the standard and FDA 21 CFR Part 820 expectations: how to audit risk management per ISO 14971, how to verify design control records tell a complete story, how to assess CAPA effectiveness, and how to prepare for the regulatory audits that follow. We share the findings that most often trip up device manufacturers and how a disciplined internal audit program catches them first.
Higher Stakes Than Most Standards
Internal audits under ISO 13485 carry consequences that go well beyond a nonconformity on a report. A weak audit program in a medical device operation does not just risk your certificate — it risks patient safety and invites FDA scrutiny. Device manufacturers operate under both ISO 13485 and, for the US market, FDA 21 CFR Part 820, and the two share DNA but are not identical. Your internal audit program has to satisfy the standard while also demonstrating the kind of control that stands up to regulatory inspection.
That means auditing not merely for the existence of procedures but for the effectiveness of the processes that most directly affect patient safety: risk management, design controls, CAPA, and post-market surveillance. An internal audit that confirms documents exist but never tests whether risk controls actually work is exactly the kind of program that lets a serious problem reach the field.
Auditing Risk Management per ISO 14971
Risk management is the backbone of medical device quality, and ISO 14971 defines how it should work. Your internal audits must verify that risk management is a living process, not a file assembled once and forgotten. Auditors should trace whether identified hazards connect to risk controls, whether those controls were verified as effective, and whether production and post-market information feeds back into the risk file as required.
A common and serious finding is a risk management file that was completed during design and never updated as complaints, CAPAs, and production data accumulated. ISO 14971 requires that post-production information be reviewed for its impact on the risk assessment. Audit for that loop specifically: pull recent complaints and field data and check whether they were evaluated against the risk file. A disconnected risk process is a patient-safety gap, and it is exactly what a rigorous internal audit should catch before a regulator does.
Verifying Design Controls and CAPA
Design controls are where many device findings originate. Your audits should verify that the design history file tells a complete, coherent story — that user needs flow to design inputs, inputs to outputs, outputs to verification and validation, and that design changes are controlled and traceable. Gaps and broken links in that chain are among the most common issues both registrars and FDA investigators find. Audit the story, not just the presence of documents.
CAPA effectiveness deserves equal scrutiny. Under ISO 13485 and Part 820, CAPA is a focal point of regulatory inspection. Audit whether root cause analysis is genuine, whether corrective actions address systemic causes, and critically whether effectiveness was verified before closure. A CAPA system that closes actions without confirming they worked is a finding waiting to happen — and in a device context, a potential patient-safety issue.
Preparing for the Regulatory Audits That Follow
A disciplined internal audit program is your best preparation for the external audits and inspections that define medical device manufacturing. When your internal auditors audit the way registrars and FDA investigators do — tracing evidence, testing effectiveness, focusing on risk, design, and CAPA — external audits hold few surprises. The findings that trip up device manufacturers are almost always ones a strong internal program would have caught first.
Build your internal audit schedule to cover the full quality system across the audit cycle, weighted toward the highest-risk processes. Ensure auditor independence and competence, feed findings into management review, and drive corrective actions to verified closure. As active third-party auditors, we build ISO 13485 internal audit programs that anticipate exactly what regulators look for — so that when the inspection comes, your system demonstrates control rather than scrambling to explain gaps. In the device world, that discipline protects your certificate, your market access, and ultimately the patients who depend on your products.